 by
October 13, 2026 update: A fake $39,318.01 ACH request
Another email using my name arrived at our accounting inbox on October 13, 2026. It said, “Please pay via ACH today,” and was signed “Dennis Yu.” Underneath was a supposed forwarded invoice request claiming an outstanding balance of $39,318.01.
I did not authorize this request. I confirmed it was spam and had it marked as spam.
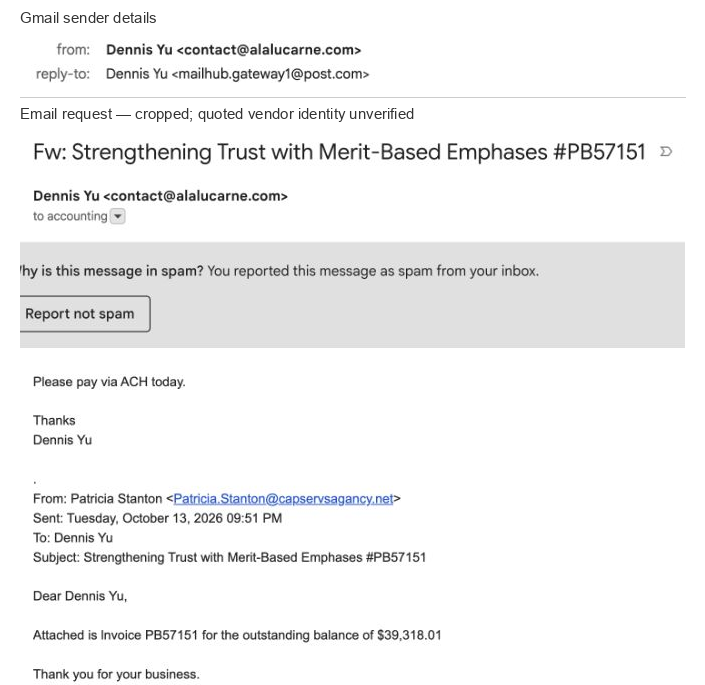
Here are the details worth checking:
- Display name: Dennis Yu
- Actual From address: contact@alalucarne.com
- Reply-To address: mailhub.gateway1@post.com
- Claimed invoice: PB57151, for $39,318.01
- Pressure: Pay by ACH “today”
The name on the email and the signature were meant to make this look like an instruction from me. The actual sender address and reply destination told a different story. A forwarded-looking block of text is easy to type into an email; it is not independent proof that a vendor sent an invoice or that I approved it.
There is another important detail: the original receiving checks recorded SPF, DKIM and DMARC passes for the sending domain. Those checks did not establish that I wrote the message or approved a payment. Google explains that spammers can authenticate mail, too.
We have not established who controlled the sending account. A domain or a person’s name appearing in a fraudulent message does not prove that its legitimate owner participated in the scam.
Make sure your accounting team checks the full sender and Reply-To addresses, matches every invoice to an approved purchase, and verifies unusual payment requests through a phone number or other channel already on file. Do not let “pay today” replace your approval process.
Original account, published August 16, 2024
This morning, our company narrowly avoided falling victim to a scam that nearly cost us $19,000.
Despite the precautions we have in place, scammers are finding new ways to deceive even the most vigilant businesses.
The scam started with an email that appeared to be from me, instructing our accounting team to pay an overdue invoice from Oracle. The email was crafted to look legitimate, complete with a fake signature line, a plausible email address, and language that mimicked typical business correspondence.
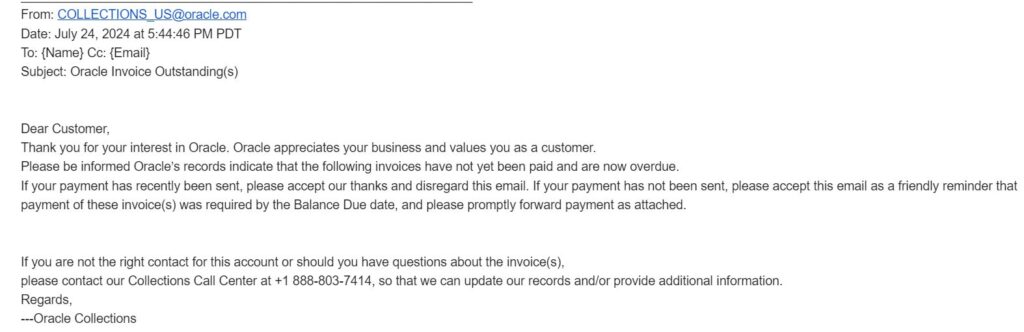
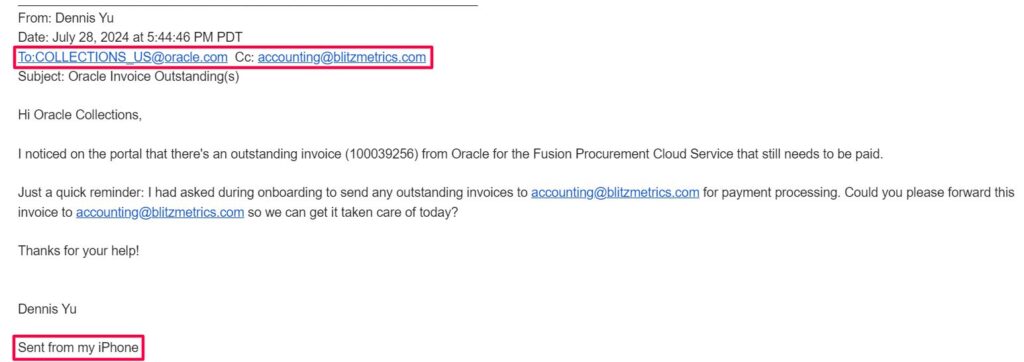
But upon closer inspection, there were several red flags:
- The email supposedly came from me, but the sender’s address wasn’t one I recognized or used. It was a spoofed email made to look convincing.
- The tone and wording of the email didn’t match my usual communication style, and it included a signature line that wasn’t mine.
- Oracle isn’t a vendor we work with, and the invoice was for a service we never purchased.
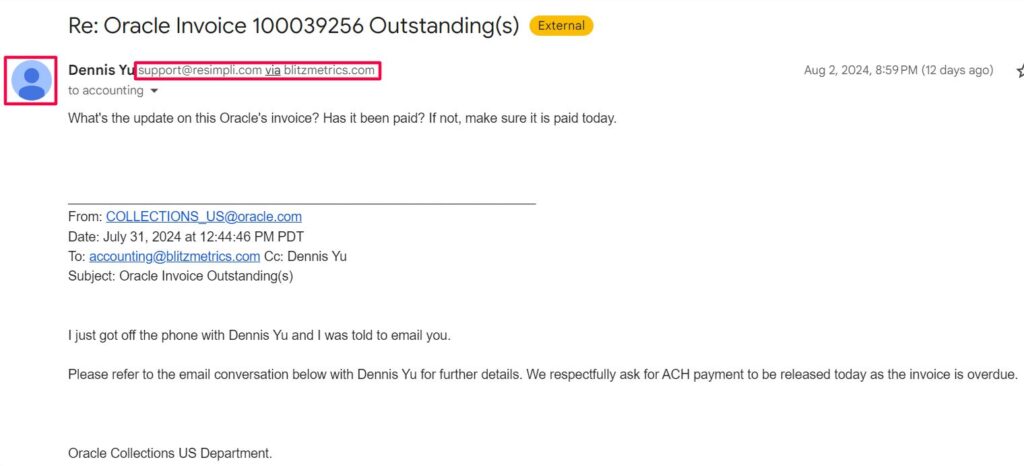
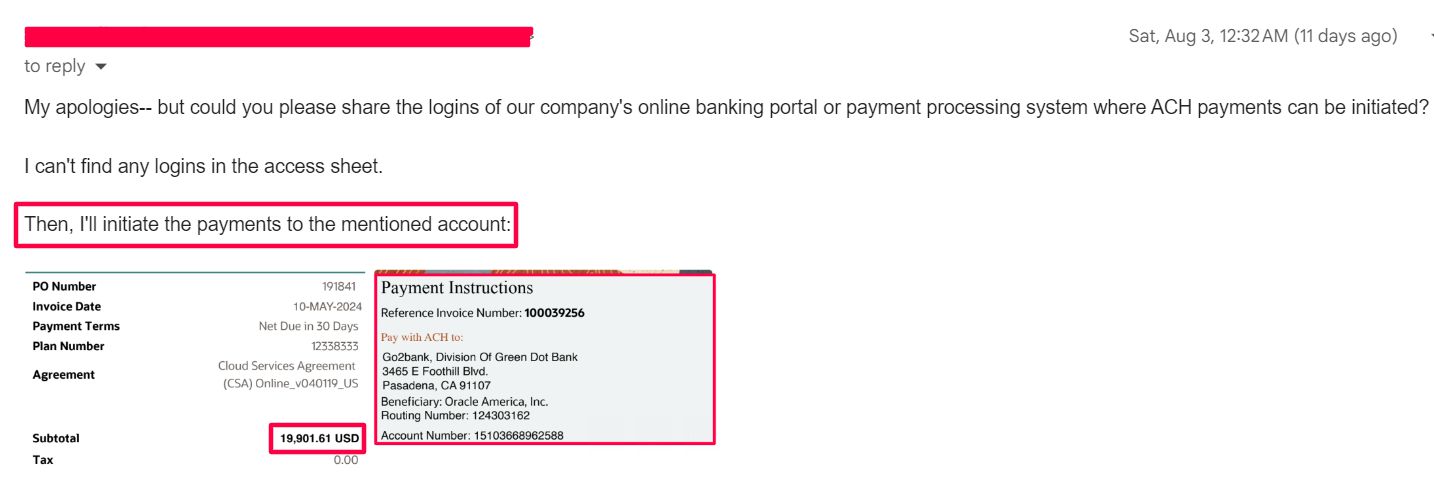
Here’s a snippet of the email thread that almost fooled us:
- From the Scammer: “What’s the update on Oracle’s invoice? Has it been paid? If not, make sure it is paid today.”
- From the Fake Oracle Collections: “I just got off the phone with Dennis Yu and was told to email you. We respectfully ask for ACH payment to be released today as the invoice is overdue.”
These emails were designed to create urgency and pressure our team into making a hasty payment without further verification. The scammers even went so far as to follow up with additional emails, reinforcing the demand for immediate payment.
Unfortunately, this is not the first time we’ve encountered such deceitful practices. Just as shocking is the experience I had with Tristan Parmley, who stole the company, I created and made it his “own”.
These scams not only affect our financial health but also erode trust within our industry. As seen in another troubling instance, where my former business partner betrayed our mutual interests for personal gain, the pattern of unethical behavior is disturbingly common.
How We Caught the Scam
Fortunately, we have a protocol for verifying large payments and checking the authenticity of any invoices from unfamiliar vendors. This process helped us quickly identify that something was off.
The Lessons We Learned
Scammers often create a sense of urgency to push you into making quick decisions. Always take a moment to verify before acting.
Look closely at email addresses, language, and other details that could indicate a phishing attempt.
Implement a strict verification process for approving payments, especially for unfamiliar vendors.
Ensure everyone in your company is aware of these tactics and knows how to handle suspicious emails.
What to Do If You’re Targeted
If you receive an email like this, take these steps:
- Engaging with scammers could lead to further attacks.
- Contact the vendor directly using known contact details, not those provided in the suspicious email.
- Notify your IT department and report the scam to relevant authorities, such as the FTC or your country’s fraud prevention agency.
Scams like this are becoming increasingly sophisticated, but with the right precautions, you can protect your business.
Stay vigilant, educate your team, and always verify before you pay.
Related scam story
- Brandon DeBoer: My $2,500 Lesson from an Influencer Who Overpromised and Disappeared
- Lane Houk and the Signal Genesys Scam: My $10K Mistake & Blame Game
Originally published .
Dennis Yu
Dennis Yu is the CEO of Local Service Spotlight, a platform that amplifies the reputations of contractors and local service businesses using the Content Factory process. He is a former search engine engineer who has spent a billion dollars on Google and Facebook ads for Nike, Quiznos, Ashley Furniture, Red Bull, State Farm, and other brands.
Dennis has achieved 25% of his goal of creating a million digital marketing jobs by partnering with universities, professional organizations, and agencies. Through Local Service Spotlight, he teaches the Dollar a Day strategy and Content Factory training to help local service businesses enhance their existing local reputation and make the phone ring.
Dennis coaches young adult agency owners serving plumbers, AC technicians, landscapers, roofers, electricians, and believes there should be a standard in measuring local marketing efforts, much like doctors and plumbers must be certified. He has appeared on 353 podcasts with 619 credited episodes — see the full list of his podcast appearances.